
CMMC Level 2 Self-Assessment Tool now available
Is your organization ready for CMMC? Start with a free self-assessment from Exemplar Cyber Advisors.
Understand Your CMMC Readiness. Plan Your Next Step.
Preparing for CMMC can feel overwhelming. Before investing in a consulting engagement, get a clearer picture of your organization's cybersecurity readiness using the free Level 2 CMMC self-assessment tool from Exemplar Cyber Advisors.
Free from beginning to end. No paid consulting engagement required.
- Understand your environment and CUI scope
- Work through cybersecurity assessment questions
- Understand potential readiness gaps
- Review your estimated SPRS score
- Prioritize your next remediation steps
- Generate a free SSP
A practical starting point for CMMC readiness.
Whether you're a small defense contractor, a subcontractor, or an organization preparing for CMMC Level 2, understanding your current position is the first step toward making a plan.
Understand Your Scope
Begin identifying the systems, information, and boundaries that may be relevant to your CMMC requirements, including environments that handle Controlled Unclassified Information (CUI).
Identify Potential Gaps
Work through cybersecurity assessment questions to identify areas where your organization may need to improve its security practices and documentation.
Plan Your Next Steps
Review your estimated SPRS score and prioritized remediation opportunities to begin building a practical CMMC readiness roadmap.
What Is CMMC Readiness?
The Cybersecurity Maturity Model Certification (CMMC) program establishes cybersecurity requirements for organizations in the Department of Defense supply chain. For organizations handling Controlled Unclassified Information (CUI), CMMC readiness commonly involves understanding applicable requirements, identifying in-scope systems, evaluating security gaps, developing required documentation, and preparing for the applicable assessment process.
CMMC Level 2 is generally associated with the 110 security requirements in NIST SP 800-171, when those requirements apply to the organization's contract and information environment. The first step is understanding where your organization stands today.
Exemplar Cyber Advisors provides a free CMMC Level 2 self-assessment tool to help defense contractors throughout the process.
See Your CMMC Readiness From Multiple Angles.
The Exemplar CMMC self-assessment tool brings together information about your environment, cybersecurity requirements, potential gaps, and remediation priorities to help you understand your next steps.
CMMC Scope and Boundary Diagram
Begin mapping the systems and environment relevant to your CMMC readiness effort. Understanding scope is an important part of determining which requirements apply and where security responsibilities belong.
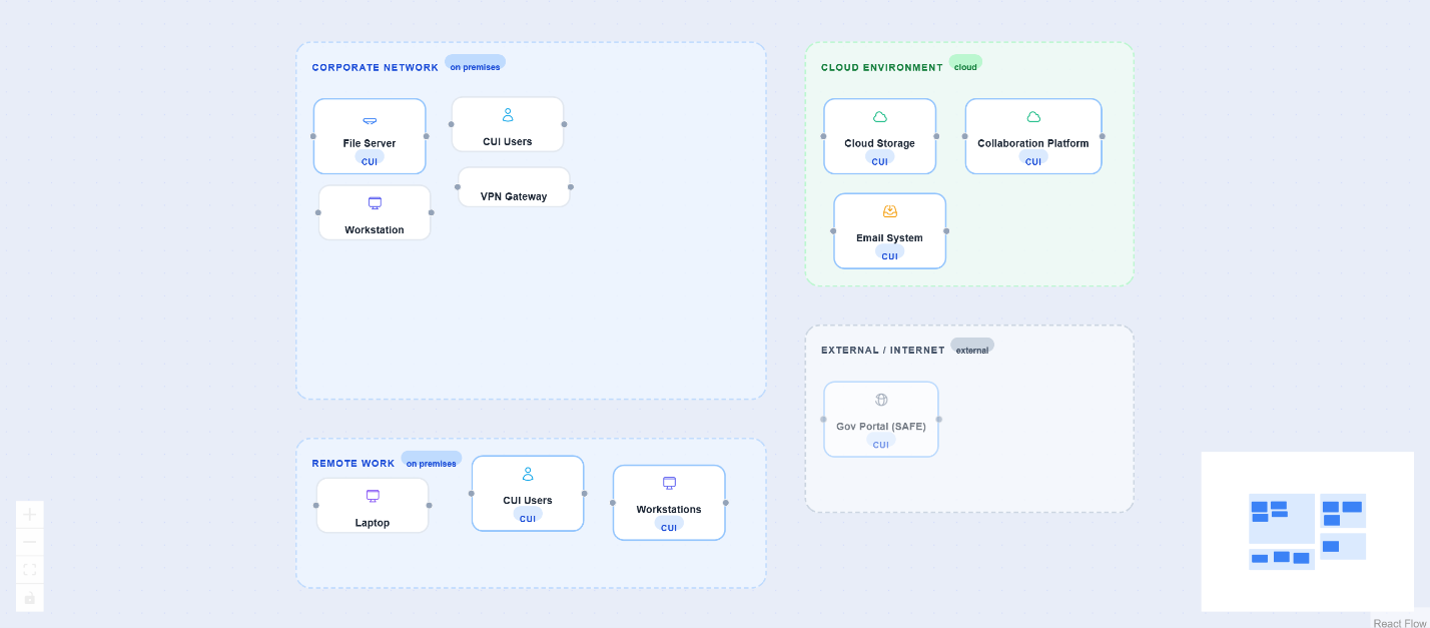
Example: Organize the systems and boundaries relevant to your CMMC readiness assessment.
Work Through SPRS Assessment Questions
Review questions aligned to the security requirements relevant to your assessment. Use the process to identify where your organization has implemented practices and where additional work may be needed.
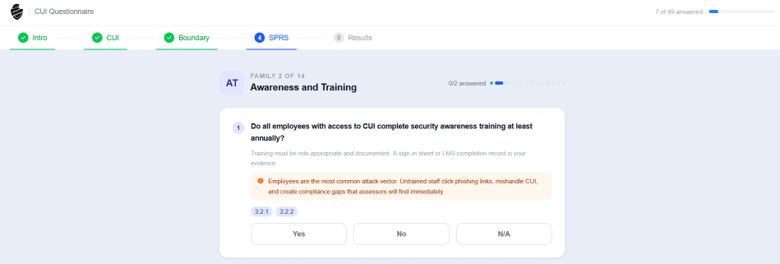
Example: Work through the assessment questions and evaluate your current security practices.
Review Your Estimated SPRS Score
Use the assessment results to understand your estimated Supplier Performance Risk System (SPRS) score. The score can help provide a starting point for understanding potential readiness gaps and prioritizing your next steps.

Example: Review your estimated score and understand where additional cybersecurity work may be needed.
Understand Potential Security Gaps
Review the areas where your organization may not yet meet applicable cybersecurity requirements. Use the results to begin organizing remediation work and determine where additional analysis may be valuable.
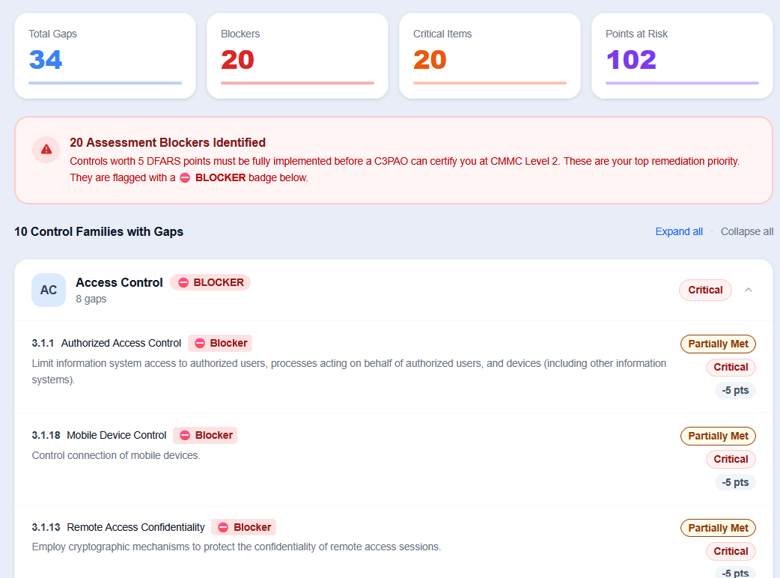
Example: Review potential gaps and identify opportunities for improvement.
Prioritize the Controls That Need Attention.
Knowing your gaps is only the beginning. Effective CMMC readiness requires a practical plan for addressing the areas that matter most to your organization.
Use the assessment results to help organize remediation priorities, understand the work ahead, and start building a more focused path toward CMMC readiness.
- Identify areas requiring additional attention.
- Organize remediation opportunities.
- Understand your next steps.
- Prepare for a more informed consulting engagement.
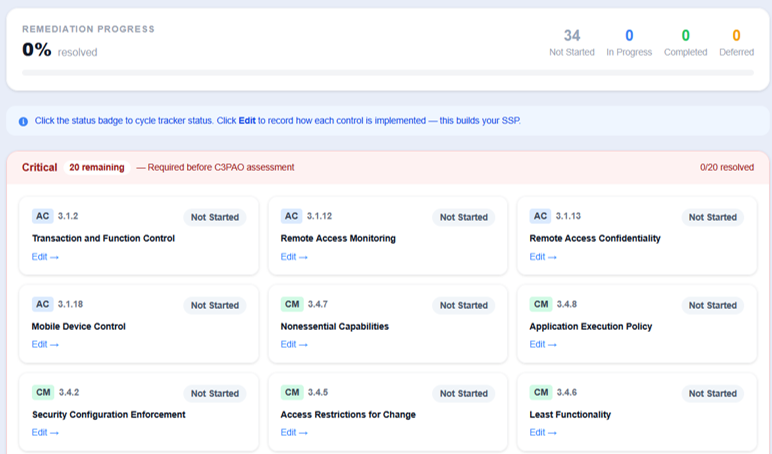
Example: Organize prioritized controls to help guide your remediation planning.
Who Should Use the CMMC Self-Assessment Tool?
This free CMMC self-assessment is designed for organizations in the Defense Industrial Base (DIB), including:
- Small and mid-sized defense contractors.
- Subcontractors working with prime contractors.
- Organizations that handle or may handle Controlled Unclassified Information (CUI).
- Companies preparing for CMMC Level 2 readiness.
- Business leaders who want to understand their cybersecurity gaps before engaging a consultant.
If you're unsure whether CMMC applies to your organization, the assessment can help you start asking the right questions and identify what to investigate next.
From Self-Assessment to CMMC Readiness.
The free tool helps you begin understanding your organization's readiness. When you need deeper analysis, documentation, or ongoing leadership, Exemplar Cyber Advisors can help.
Explore Your Readiness
Start with a self-guided assessment, understand potential gaps, review your estimated score, and organize your next steps.
CMMC Gap Assessment
Get a deeper, consultant-led evaluation of your organization's cybersecurity readiness, requirements, and areas for improvement.
CMMC Readiness Support
Build a practical path toward readiness with support for security strategy, documentation, remediation, and ongoing cybersecurity leadership.
CMMC Self-Assessment Questions
What is a CMMC self-assessment?
A CMMC self-assessment is a self-guided process for evaluating an organization's cybersecurity practices against applicable CMMC requirements. It can help identify potential gaps and support readiness planning. It is not a substitute for an official CMMC assessment or certification.
Is the Exemplar CMMC self-assessment tool free?
Yes. Exemplar Cyber Advisors provides a free CMMC self-assessment tool to help defense contractors begin understanding their cybersecurity readiness and next steps.
What is an SPRS score?
The Supplier Performance Risk System (SPRS) score is associated with cybersecurity self-assessment information used in the Department of Defense supply chain. The Exemplar tool provides an estimated score based on assessment responses to help support readiness planning.
What is CMMC Level 2?
CMMC Level 2 is associated with the protection of Controlled Unclassified Information (CUI) and the applicable security requirements in NIST SP 800-171. The requirements that apply to an organization depend on its contract and information environment.
Does Exemplar Cyber Advisors provide CMMC readiness consulting?
Yes. Exemplar Cyber Advisors provides CMMC readiness and cybersecurity advisory services, including gap assessments, readiness planning, documentation support, remediation guidance, and ongoing vCISO leadership.
Is the free self-assessment an official CMMC certification?
No. The Exemplar self-assessment is a readiness planning resource. It is not a C3PAO assessment, CMMC certification, or official determination of compliance.
Understand Your Readiness Before You Invest in the Next Step.
Use the free Exemplar CMMC self-assessment to begin identifying potential gaps, understanding your environment, and planning your next steps toward CMMC readiness.
Start Your Free CMMC Self-Assessment Talk With a CMMC AdvisorThe Exemplar CMMC self-assessment is a readiness planning resource. It is not an official CMMC assessment, certification, or determination of compliance. CMMC requirements may vary based on applicable contracts and information handled.